Zero to Patch: A Practical Patch Management Checklist
A practical, step-by-step patch management checklist for small and medium teams: inventory, prioritize, test, automate, and verify to reduce vulnerability exposure and speed remediation.
Beyond CVSS: Contextual Vulnerability Prioritization
Beyond CVSS: Contextual Vulnerability Prioritization Introduction CVSS is a useful baseline for understanding vulnerability severity, but it’s only part of the story. True prioritization needs context: exploit availability, asset criticality, network exposure, business impact, and compensating controls. This article lays out a practical framework you can apply today to make triage decisions faster and more […]
Working From Home: Essential Security Tips for All Remote Workers
In today’s interconnected world, remote work has become a norm for many professionals. While it offers numerous benefits such as flexibility and improved work-life balance, it also comes with its share of risks. Securing your home office environment is not just a technical necessity; it’s a crucial aspect of maintaining the integrity and confidentiality of […]
Port Scanning with Python, Bash, and PowerShell
Network scanning is a fundamental process in cybersecurity, allowing security professionals to identify open ports, services, and potential vulnerabilities within a network. It is an essential step in both defensive and offensive security operations, enabling organizations to assess their attack surface and identify potential weaknesses before malicious actors can exploit them. Among the most widely […]
Set Up a Successful Bug Bounty Team
In today’s digital age, cybersecurity is more crucial than ever. A bug bounty program is an innovative approach where organizations invite ethical hackers to identify and report security vulnerabilities in their software, applications, and systems. This not only helps in fortifying defenses but also encourages a culture of continuous improvement and vigilance. Having a dedicated […]
Enhancing DevOps Security: Strategies for Securing CI/CD Pipelines
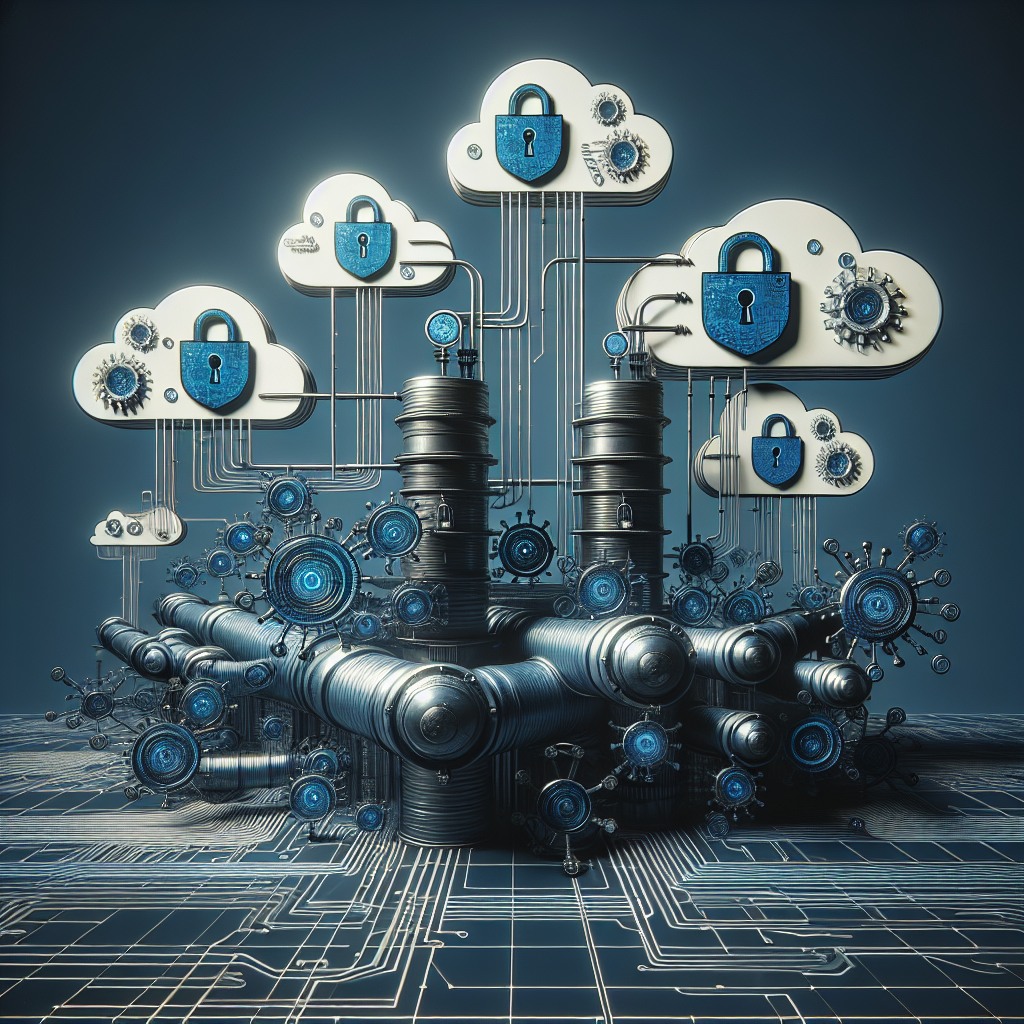
Enhancing DevOps Security: Strategies for Securing CI/CD Pipelines Introduction DevOps has revolutionized the software development process, enabling organizations to deliver high-quality software at a faster pace. However, with the increasing adoption of DevOps, the need for robust security measures has become more critical. CI/CD pipelines, which are the backbone of DevOps, are particularly vulnerable to […]
Step-by-Step Guide to Installing and Configuring Velociraptor for Digital Forensics and Incident Response
Introduction A how-to guide for installing and configuring Velociraptor, a tool used in digital forensics and incident response (DFIR), can be quite technical. Here’s a step-by-step guide to help you set up Velociraptor in a typical environment. This guide assumes a basic understanding of systems administration and network security, which should align well with your […]
Understanding DevSecOps: An In-Depth Guide to Integrating Security in DevSecOps Practices
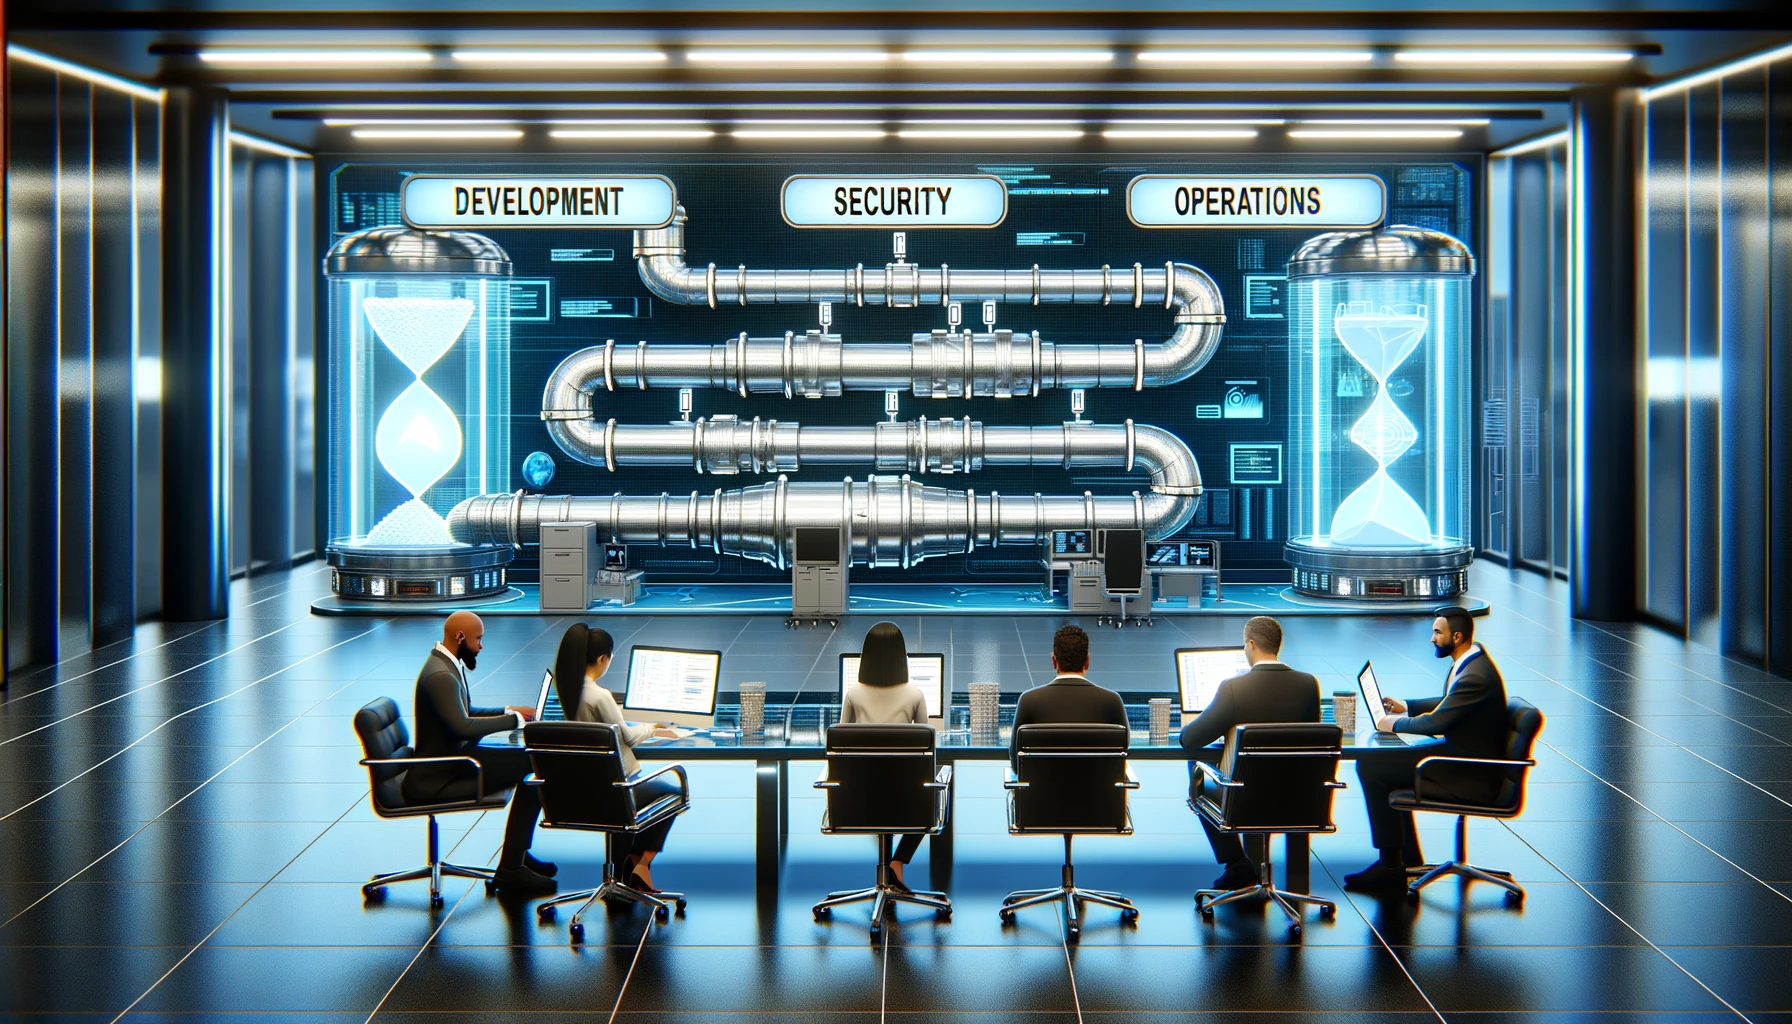
Integrating Security into DevOps: The Critical Role of DevSecOps Key Takeaways: Understanding DevSecOps: Merging development, security, and operations for enhanced cybersecurity. Benefits of DevSecOps: Streamlined processes, improved security, and accelerated development cycles. Implementing DevSecOps: Key strategies and tools for successful integration. What is DevSecOps? In an era where digital transformation is paramount, the concept of […]
A Deep Dive Into APT34 (OilRig): Discovering Iranian Hackers
Introduction In today’s digitally interconnected world, understanding the dynamics of cybersecurity threats is crucial. Among these threats, Advanced Persistent Threat 34 (APT34), also known as OilRig, stands out as a sophisticated and covert menace. This blog post delves into the world of APT34, unraveling its complexities and implications for global cybersecurity. As businesses and governments […]
Installing the Kali Linux VM: Enhance Your Cybersecurity Skills With VMware Workstation.
Introduction The easiest way to install Kali is on a VM. The first thing that you want to do so go to the Offensive Security website and download the Kali VM for either a VMware workstation or Virtual Box. Installing Kali on a VM allows you to be more flexible with your installation by providing […]