Dominion Cyber
Cybersecurity Articles & Insights
Practical security guides, threat deep-dives, and hands-on how-tos for defenders, engineers, and the security-curious.
Deep Dive into Intrusion Detection Systems (IDS): Signature vs. Anomaly-based Detection.
Key Takeaways: Signature-based IDS: Signature-based intrusion detection systems rely on pre-defined patterns or signatures to identify known threats. These systems are effective in detecting known attacks and are relatively…
Modern DDoS Attacks: Understanding Multi-vector Strategies and Defense Mechanisms.
Key Takeaways: Modern DDoS attacks are becoming more sophisticated and diverse, utilizing multi-vector strategies to overwhelm target networks and exploit vulnerabilities in various protocols and applications. Application-level attacks, such as…
Exploring Cyber Threat Landscapes: Region-specific Threats, Actors, and Responses.
Key Takeaway: Understanding region-specific cyber threats is crucial: Different regions face unique cyber threats and challenges. It is important to have a comprehensive understanding of these threats to develop effective…
Physical Security in the Digital World: Safeguarding Data Centers, Offices, and Hardware.
Key Takeaway: Physical security is crucial in the digital world: Safeguarding data centers, offices, and hardware is essential to protect sensitive information from physical threats such as theft, vandalism, and…
Exploring the Dark Web: Understanding Its Infrastructure, Operations, and Threats.
Key Takeaway: The Dark Web is a hidden part of the internet that requires special software to access. It is used for various purposes, including illegal activities, anonymous communication,…
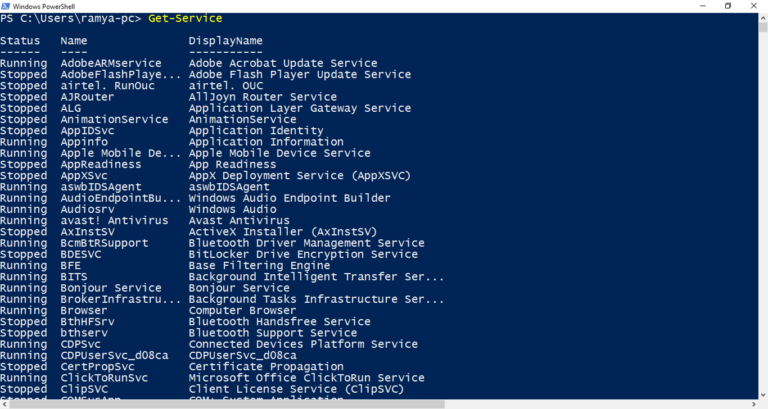
PowerShell for Pentesters: Harnessing Microsoft’s Tool for Advanced Exploitation.
Key Takeaway: PowerShell has become a powerful tool for pentesters, providing advanced exploitation capabilities. Its rise in popularity is driven by its versatility and extensive functionality. PowerShell can be…
Unmasking Equation Group: Shedding Light on Cybersecurity’s Green Guardians
Introduction While not directly confirmed, this group is widely believed to be affiliated with the U.S. National Security Agency (NSA). They are known for their sophisticated tools and tactics, including…
Unmasking Turla (Snake, Uroburos) The Shadowy World of a State Sponsored Cyber Espionage
Introduction This group is believed to be Russian-sponsored and has been active for several years, targeting embassies, military entities, and research institutions mainly in the Middle East and Europe. Turla,…
Unveiling OceanLotus APT32 Investigating Suspected Ties To The Vietnamese Government In Cyber Espionage
Introduction Originating from Vietnam, OceanLotus is believed to be state-sponsored and has targeted foreign companies investing in Vietnam’s manufacturing, consumer products, and hospitality sectors. Cyber espionage is a growing threat…